

provider stringlengths 4 29 | product_or_protocol stringlengths 8 47 | control_type stringclasses 9
values | field_or_setting stringlengths 11 169 | unit stringlengths 5 120 | period_options stringlengths 10 93 | enforcement_point stringlengths 15 144 | evidence_url stringlengths 31 156 | verbatim_quote stringlengths 20 173 | accessed_date stringdate 2026-09-29 00:00:00 2026-10-02 00:00:00 | notes stringlengths 23 353 |
|---|---|---|---|---|---|---|---|---|---|---|
AP2 (Agent Payments Protocol) | AP2 spec / Google reference SDK | amount_cap_per_tx | amount_range.max (constraint) | minor units (cents) | not stated | API server-side (evaluated by BudgetEvaluator/AmountRangeEvaluator in the reference SDK) | https://raw.githubusercontent.com/google-agentic-commerce/AP2/e1ea56db72a6385bce3e5c1112b3a56ce60acb43/code/sdk/schemas/ap2/open_payment_mandate.json | Maximum allowed amount in minor (cents) unit of currency. | 2026-09-29 | Pinned commit e1ea56d, lines 135-137 per prior verified sources-check (ap2-mandate-gotchas). |
AP2 (Agent Payments Protocol) | AP2 spec / Google reference SDK | amount_cap_per_period | budget.max (constraint) | major units (multiplied by 100 internally to get minor units) | not stated in schema (recurrence handled via separate agent_recurrence constraint) | API server-side (BudgetEvaluator in the reference SDK) | https://raw.githubusercontent.com/google-agentic-commerce/AP2/e1ea56db72a6385bce3e5c1112b3a56ce60acb43/code/sdk/schemas/ap2/open_payment_mandate.json | Maximum amount for the budget. | 2026-09-29 | Unit mismatch vs amount_range.max is a documented gotcha (see README Gotchas): schema text alone does not state the unit; code (constraints.py line 307, budget_max_cents = int(self.constraint.max * 100)) shows budget.max is major units. |
AP2 (Agent Payments Protocol) | AP2 spec | human_approval | Cart Mandate / Payment Mandate signing | not applicable | not applicable | client-side (user signs mandate) then verified server-side | https://cloud.google.com/blog/products/ai-machine-learning/announcing-agents-to-payments-ap2-protocol | After the agent presents a cart with the shoes you want, your approval signs a Cart Mandate | 2026-09-29 | Google's own launch post describing the human-in-the-loop approval step. |
AP2 (Agent Payments Protocol) | AP2 spec | other | constraints array (presence-driven evaluation) | not applicable | not applicable | API server-side | https://raw.githubusercontent.com/google-agentic-commerce/AP2/e1ea56db72a6385bce3e5c1112b3a56ce60acb43/code/sdk/python/ap2/sdk/constraints.py | for constraint in open_mandate.constraints: evaluator = create_payment_evaluator( | 2026-09-29 | Only constraints present in the array are evaluated; a withheld constraint is not enforced (flagged as a gotcha in AP2 issue #339). |
Stripe | Stripe Issuing (Card object) | amount_cap_per_period | spending_controls.spending_limits[].amount + .interval | smallest currency unit of the card currency | per_authorization, date-based intervals (start at midnight UTC); full enum on the Card object | authorization-time (Stripe declines before/at the issuing_authorization.request) | https://docs.stripe.com/issuing/controls/spending-controls | Spending limit rules limit the total amount of spending for categories over intervals of time. | 2026-09-29 | PM 09-29: replaced the empty-array excerpt with the spending-controls guide. Unit quote: "This amount is in the card’s currency and in the smallest currency unit". |
Stripe | Stripe Issuing (Card object) | amount_cap_per_tx | spending_controls.spending_limits[].interval = per_authorization | smallest currency unit of the card currency | per_authorization | authorization-time (Stripe declines before/at the issuing_authorization.request) | https://docs.stripe.com/issuing/controls/spending-controls | spending_controls[spending_limits][0][interval]=per_authorization | 2026-09-29 | PM 09-29: from the cURL example on the spending-controls guide (raw page source). |
Stripe | Stripe Issuing (Card object) | category_block | spending_controls.allowed_categories / spending_controls.blocked_categories | not applicable | not applicable | authorization-time at card network | https://docs.stripe.com/api/issuing/cards/object | "allowed_categories": [],
"blocked_categories": [], | 2026-09-29 | Confirmed field names in the Card object JSON schema on the live API reference page. |
Stripe | Stripe Issuing | other | not documented (marketing copy only) | not applicable | not applicable | authorization-time at card network, via real-time webhook authorization | https://docs.stripe.com/issuing | Real-time authorizations : View and control authorization requests as they happen, using webhooks. | 2026-09-29 | Describes the webhook-based real-time authorization control point; general product page, not the API reference. |
Privacy.com | Privacy Cards API | amount_cap_per_tx | spend_limit (with spend_limit_duration=TRANSACTION) | minor units (cents) | ANNUALLY, FOREVER, MONTHLY, TRANSACTION | authorization-time at card network | https://developers.privacy.com/docs/cards | spend_limit Amount (in cents) to limit approved authorizations. Transaction requests above the spend limit will be declined. | 2026-09-29 | Reused from prior verified sources-check (virtual-cards-for-ai-agents). |
Privacy.com | Privacy Cards API | amount_cap_per_period | spend_limit_duration | not applicable (enum) | ANNUALLY, FOREVER, MONTHLY, TRANSACTION | authorization-time at card network | https://developers.privacy.com/docs/cards | spend_limit_duration ANNUALLY , FOREVER , MONTHLY , TRANSACTION . | 2026-09-29 | Same field family as spend_limit; duration enum sets the reset period. |
Privacy.com | Privacy Cards API | merchant_allowlist | type=MERCHANT_LOCKED | not applicable | not applicable | authorization-time at card network | https://developers.privacy.com/docs/cards | type MERCHANT_LOCKED , SINGLE_USE , DIGITAL_WALLET . | 2026-09-29 | Card type enum; MERCHANT_LOCKED locks the card to the first merchant it's used at. |
Privacy.com | Privacy Cards API | single_use | type=SINGLE_USE | not applicable | not applicable | authorization-time at card network | https://developers.privacy.com/docs/cards | type MERCHANT_LOCKED , SINGLE_USE , DIGITAL_WALLET . | 2026-09-29 | Same enum as above; SINGLE_USE closes the card after one approved authorization. |
Lithic | Lithic Cards API | amount_cap_per_period | spend_limit + spend_limit_duration | cents (per Privacy/industry convention; not explicitly restated on this page) | ANNUALLY, FOREVER, MONTHLY, TRANSACTION | authorization-time at card network | https://docs.lithic.com/docs/spend-limits | Cards support a single spend_limitwith spend_limit_duration of ANNUALLY, FOREVER, MONTHLY, or TRANSACTION. | 2026-09-29 | Rendered via Playwright 2026-09-29; docs.lithic.com is a JS-rendered site. |
Lithic | Lithic Accounts API | amount_cap_per_period | account-level spend limits (daily, monthly, lifetime) | not stated in this excerpt | daily, monthly, lifetime | authorization-time at card network | https://docs.lithic.com/docs/spend-limits | Accounts support multiple concurrent spend limits: daily, monthly, and lifetime. | 2026-09-29 | Account-level limits apply across all cards on the account. |
Lithic | Lithic Authorization Rules (Velocity Limit) | amount_cap_per_period | limit_amount | cents | configurable period window (e.g. daily) via the rule's period object | authorization-time at card network (Lithic-hosted Auth Rules engine) | https://docs.lithic.com/docs/velocity-limit-rules | limit_amount: the maximum total spend allowed within the period, in cents. Set to null for no amount limit | 2026-09-29 | VELOCITY_LIMIT rule type; scope can be CARD or ACCOUNT. |
Lithic | Lithic Authorization Rules (Velocity Limit) | other | limit_count | not applicable (count, not amount) | same period window as limit_amount | authorization-time at card network | https://docs.lithic.com/docs/velocity-limit-rules | limit_count: the maximum number of transactions allowed within the period. Set to null for no count limit | 2026-09-29 | Transaction-count cap rather than an amount cap; paired with limit_amount in the same rule object. |
Lithic | Lithic Authorization Rules (Velocity Limit) | other | scope (CARD or ACCOUNT) | not applicable | not applicable | authorization-time at card network | https://docs.lithic.com/docs/velocity-limit-rules | CARD: tracks each card's spend independently | 2026-09-29 | Sets whether the velocity limit is tracked per-card or pooled across the whole account. |
Lithic | Lithic Authorization Rules | merchant_allowlist | MERCHANT_LOCK (rule type) | not applicable | not applicable | authorization-time at card network | https://docs.lithic.com/docs/authorization-rules-v2 | You may also see rules with the MERCHANT_LOCK type (often Lithic-managed) in rule listings. | 2026-09-29 | Rendered via Playwright 2026-09-29. Listed/fetchable but the docs state MERCHANT_LOCK rules cannot be created or updated through this API. |
Lithic | Lithic Authorization Rules (Conditional Action) | category_block | CONDITIONAL_ACTION rule keyed on MCC | not applicable | not applicable | authorization-time at card network | https://docs.lithic.com/docs/authorization-rules-v2 | By defining rules based on high-signal attributes like MCC, country, currency, and risk score, you can enforce business-specific authorization logic | 2026-09-29 | MCC = Merchant Category Code; exact JSON parameter name for the MCC condition was not captured in this excerpt. |
AgentCard | Agentcard CLI | amount_cap_per_period | cards set-limit (CLI command) | cents (consistent with amount_cents) | not applicable (total limit on a multi-use card) | API server-side | https://docs.agentcard.sh/tools/cli/cards-set-limit | Change a multi-use card's total spending limit | 2026-09-29 | Reused from prior verified sources-check. |
Crossmint | Crossmint Agent Cards / Agent Wallets | revocation | not documented (described only as an 'allowance' concept, no field name given on this page) | not applicable | not applicable | not stated on this page (see enforcement row below) | https://docs.crossmint.com/agents/overview | Every allowance is scoped, explicit, and revocable | 2026-09-29 | Overview/marketing page; exact API field for scoping/revoking an allowance not shown here. |
Crossmint | Crossmint Agent Cards / Agent Wallets | other | not documented (enforcement description only) | not applicable | not applicable | authorization-time at card network (Visa/Mastercard) for cards; onchain for wallets | https://docs.crossmint.com/agents/overview | Card limits hold at Visa and Mastercard, wallet limits hold onchain | 2026-09-29 | Distinguishes card-rail enforcement (network-side) from wallet-rail enforcement (onchain), a useful enforcement-point data point even without an exact field name. |
Coinbase | CDP Agentic Wallet (MCP) | amount_cap_per_tx | "Max per call" (wallet UI setting; API field name not documented on this page) | not stated (example given in USD, e.g. $0.05) | not applicable | not stated on this page (policy engine enforces before signing; TEE/enclave claims found only in third-party summaries, not this primary source) | https://docs.cdp.coinbase.com/agentic-wallet/mcp/faq | Max per call: Max for a single payment (e.g., $0.05) | 2026-09-29 | From the FAQ's 'How do spending limits work?' section, set manually in the wallet UI. |
Coinbase | CDP Agentic Wallet (MCP) | amount_cap_per_period | "Max per session" (wallet UI setting; API field name not documented on this page) | not stated (example given in USD, e.g. $5.00) | per session (session boundary not further defined on this page) | not stated on this page | https://docs.cdp.coinbase.com/agentic-wallet/mcp/faq | Max per session: Total session limit (e.g., $5.00) | 2026-09-29 | Same FAQ section as the per-call limit; both are set in the wallet UI, not via a documented API parameter. |
Coinbase | CDP Agentic Wallet (MCP) | other | not documented | not applicable | not applicable | client-side SDK / wallet UI | https://docs.cdp.coinbase.com/agentic-wallet/mcp/faq | Agents respect these limits but can’t change them. | 2026-09-29 | States the agent cannot self-modify its own limits; doesn't specify the enforcement mechanism (TEE, contract, or server policy). |
Circle | Circle Agent Wallets (CLI) | amount_cap_per_period | --daily / --weekly / --monthly (circle wallet limit set flags) | USDC (major units) | daily, weekly, monthly | client-side SDK / CLI, enforced by Circle's wallet backend | https://raw.githubusercontent.com/circlefin/skills/58ab8648bb1ae9d037a3bf5197ad3bb01262f5b1/plugins/circle/skills/agent-wallet-policy/SKILL.md | Shows the current per-tx, daily, weekly, and monthly USDC caps (`null` for any unset tier). | 2026-09-29 | Pinned commit 58ab8648. |
Circle | Circle Agent Wallets (CLI) | other | monotonic ordering rule across the four cap tiers | not applicable | not applicable | client-side SDK / CLI | https://raw.githubusercontent.com/circlefin/skills/58ab8648bb1ae9d037a3bf5197ad3bb01262f5b1/plugins/circle/skills/agent-wallet-policy/SKILL.md | Limits must be **monotonic**: `per-tx ≤ daily ≤ weekly ≤ monthly`. | 2026-09-29 | Pinned commit 58ab8648. Gotcha: setting per-tx higher than daily (etc.) is rejected. |
Circle | Circle Agent Wallets (CLI) | human_approval | OTP confirmation on `circle wallet limit set` / `reset` | not applicable | not applicable | client-side CLI (interactive terminal, human-only OTP entry) | https://raw.githubusercontent.com/circlefin/skills/58ab8648bb1ae9d037a3bf5197ad3bb01262f5b1/plugins/circle/skills/agent-wallet-policy/SKILL.md | Setting or resetting limits requires OTP confirmation in an interactive terminal session | 2026-09-29 | Pinned commit 58ab8648. From the skill's YAML frontmatter description. |
Circle | Circle Agent Wallets (CLI) | merchant_allowlist | recipient allowlists / contract blocklists (custom spending policies) | not applicable | not applicable | not stated (Circle wallet backend) | https://developers.circle.com/agent-stack/agent-wallets | Custom spending policies Set transfer limits, recipient allowlists, and contract blocklists per agent wallet. | 2026-09-29 | Product page; exact API/CLI field name for the allowlist/blocklist entries not shown on this page. |
Tempo | Tempo Wallet CLI | amount_cap_per_tx | --max-spend (tempo request flag) | not stated (example shown in dollars, e.g. 1.00) | per request | client-side SDK / CLI | https://tempo.xyz/developers/docs/wallet/use-with-agents | --max-spend and scoped access keys let you enforce budgets per request and per key. | 2026-09-29 | Caps an individual paid request; distinct from the protocol-level per-key TokenLimit below. |
Tempo | Tempo Account Keychain (protocol) | amount_cap_per_period | TokenLimit.amount (within KeyRestrictions.limits[]) | TIP20 token units (protocol-level, not restated as USD) | one-time (period=0) or recurring (period>0, in seconds) | onchain (Account Keychain precompile) | https://tempo.xyz/developers/docs/protocol/transactions/AccountKeychain | struct TokenLimit {
address token;
uint256 amount;
uint64 period;
} | 2026-09-29 | Per-access-key, per-token spending limit enforced at the protocol layer via the AccountKeychain precompile. |
Tempo | Tempo Account Keychain (protocol) | expiry | KeyRestrictions.expiry | not applicable (timestamp) | not applicable | onchain (Account Keychain precompile) | https://tempo.xyz/developers/docs/protocol/transactions/AccountKeychain | struct KeyRestrictions {
uint64 expiry;
bool enforceLimits;
TokenLimit[] limits;
bool allowAnyCalls;
CallScope[] allowedCalls;
} | 2026-09-29 | Each access key (scoped for an agent) carries its own expiry alongside its spending limits. |
Payman | Payman Dashboard Policies | amount_cap_per_tx | Per Transaction (policy spend control) | not stated (currency-agnostic in the docs example, ₹1,000 used for the threshold example) | not applicable | not stated (Payman policy engine, described as a server-side "financial firewall") | http://web.archive.org/web/20251118161108/https://docs.paymanai.com/dashboard-guide/policies | Per Transaction Maximum amount allowed per single payment | 2026-09-29 | docs.paymanai.com returned a Cloudflare 526 (invalid origin SSL cert) on 2026-09-29 when fetched directly; this Wayback Machine snapshot (captured 2025-11-18) is used as the accessible copy of the same official page and returns HTTP 200. |
Payman | Payman Dashboard Policies | amount_cap_per_period | Daily Limit / Monthly Limit (policy spend controls) | not stated | daily, monthly | not stated (Payman policy engine) | http://web.archive.org/web/20251118161108/https://docs.paymanai.com/dashboard-guide/policies | Daily Limit Maximum total amount allowed per day Monthly Limit Maximum total amount allowed per month | 2026-09-29 | Wayback Machine snapshot used; see note on prior row. |
Payman | Payman Dashboard Policies | human_approval | Threshold (policy spend control) | not stated | not applicable | not stated (Payman policy engine) | http://web.archive.org/web/20251118161108/https://docs.paymanai.com/dashboard-guide/policies | Threshold Amount above which manual approval is needed | 2026-09-29 | Wayback Machine snapshot used; see note on first Payman row. Example given elsewhere on the page: a ₹1,000 threshold triggers manual approval above that amount. |
Skyfire | Skyfire KYA-PAY token | amount_cap_per_tx | amt (claim) | currency units (not minor units) | not applicable (per-token cap) | API server-side (seller service validates the token before granting access/settling payment) | https://docs.skyfire.xyz/docs/pay-token | amt JSON string representing token amount in currency units. | 2026-09-29 | Rendered via Playwright 2026-09-29 (docs.skyfire.xyz is a JS-rendered ReadMe.io site). |
Skyfire | Skyfire KYA-PAY token | other | mnr (claim) | not applicable (a request count, not a currency amount) | not applicable | API server-side | https://docs.skyfire.xyz/docs/pay-token | mnr OPTIONAL - JSON number representing maximum number of requests when sps is pay_per_use. | 2026-09-29 | A usage-count cap tied to the pay_per_use pricing model, distinct from the dollar-amount cap (amt). |
Skyfire | Skyfire KYA-PAY token | expiry | exp (claim) | not applicable (Unix timestamp) | not applicable | API server-side | https://docs.skyfire.xyz/docs/common-token-claims | exp (expiration time) Identifies the expiration time on or after which the JWT MUST NOT be accepted for processing. | 2026-09-29 | Rendered via Playwright 2026-09-29. Common claim shared by kya, pay, and kya-pay token types. |
x402 | x402 protocol (HTTP transport v1, exact scheme) | other | maxAmountRequired | not stated in this file (example "10000" is atomic/minor units of the named asset, e.g. USDC) | not applicable | API server-side (verified by the facilitator before settlement) | https://raw.githubusercontent.com/coinbase/x402/dd927a26cfefc98c24b3ec38b3a8f204dad0c60d/specs/transports-v1/http.md | "maxAmountRequired": "10000", | 2026-09-29 | Pinned commit dd927a2. Field appears inside the `accepts[]` array of the HTTP 402 PaymentRequirementsResponse body; the `exact` scheme requires the transferred amount to equal this value exactly. PM 09-29: this is a server-declared price ceiling in the 402 response, not a payer-set spending limit; payer-side caps must ... |
x402 | x402 protocol (upto scheme) | amount_cap_per_tx | amount (PaymentRequirements, upto scheme, phase-dependent) | not stated in this file | not applicable (per-request/per-call ceiling for metered usage) | API server-side (facilitator enforces at settlement) | https://raw.githubusercontent.com/coinbase/x402/dd927a26cfefc98c24b3ec38b3a8f204dad0c60d/specs/schemes/upto/scheme_upto.md | `upto` is a scheme that authorizes a transfer of up to a **maximum amount** of funds from a client to a resource server. | 2026-09-29 | Pinned commit dd927a2. At verification time `amount` is the client-authorized maximum; at settlement time the same field carries the actual charge, which the facilitator MUST cap at that maximum. |
x402 | x402 protocol (upto scheme) | other | amount (settlement-time value MUST be <= verification-time maximum) | not stated in this file | not applicable | API server-side (facilitator) | https://raw.githubusercontent.com/coinbase/x402/dd927a26cfefc98c24b3ec38b3a8f204dad0c60d/specs/schemes/upto/scheme_upto.md | The settled amount MUST be less than or equal to the authorized maximum. | 2026-09-29 | Pinned commit dd927a2. Enforcement rule for metered/variable-usage payments (e.g. paying per token generated). |
Visa | Visa Intelligent Commerce | other | not documented (no public field-level schema found) | not applicable | not applicable | not stated (described generally as agent token authorizing "specific transaction types under specific spend limits") | https://developer.visa.com/use-cases/visa-intelligent-commerce-for-agents | Payment Instructions | 2026-09-29 | Developer portal describes spend limits, merchant categories, and required approvals at a product/marketing level; no public API reference with concrete field names for a spend-limit parameter was found as of 2026-09-29. |
Mastercard | Mastercard Agent Pay for Machines | other | not documented (no public field-level schema found) | not applicable | not applicable | not stated on this page | http://web.archive.org/web/20260918180921/https://www.mastercard.com/us/en/business/artificial-intelligence/mastercard-agent-pay/agent-pay-for-machines.html | Agent permissions and spending limits are defined upfront to bound authority. | 2026-09-29 | www.mastercard.com returned HTTP 403 to a direct fetch on 2026-09-29 (bot protection); this Wayback Machine snapshot (captured 2026-09-18) is used as the accessible copy of the same official marketing page. No public developer reference with an exact spend-limit field name was found. |
Pink Agentic AI Payments | Pink sandbox API/MCP (by PinkWallet) | amount_cap_per_tx | rule.min / rule.max with window: "tx" | USD-equivalent (major units) | tx (single payment) | API server-side (before a credential is issued) | https://pinkwallet.com/agentic/developers/policy-rules-reference/ | min / max numbers in USD-equivalent; max: null = no upper bound Inclusive range the measured value must fall in. | 2026-10-02 | Publisher (PinkWallet), self-documented. Stage: early access / public sandbox; production not yet available. |
Pink Agentic AI Payments | Pink sandbox API/MCP (by PinkWallet) | amount_cap_per_period | rule.window ("day"/"month") with min/max; plus a per-agent monthly budget and a company-wide daily ceiling, both checked as circuit breakers before any rule is evaluated | USD-equivalent (major units, rule); currency of the vault (monthly budget / daily ceiling, unit not separately restated) | tx, day, month (rule window); plus a standing monthly budget and a company daily ceiling | API server-side (before a credential is issued) | https://pinkwallet.com/agentic/developers/policy-rules-reference/ | Monthly budget. Spent this month plus this amount must not exceed the agent's budget. | 2026-10-02 | Publisher (PinkWallet), self-documented. Stage: early access / public sandbox; production not yet available. Company daily ceiling, same source: "Company daily ceiling. All agents together, per day." |
Pink Agentic AI Payments | Pink sandbox API/MCP (by PinkWallet) | merchant_allowlist | rule.payee (approved · new · list of payee ids) | not applicable | not applicable | API server-side (before a credential is issued) | https://pinkwallet.com/agentic/developers/policy-rules-reference/ | payee any · approved · new · cat:<category> · list of payee ids approved = on the payee list; new = not on it; | 2026-10-02 | Publisher (PinkWallet), self-documented. Stage: early access / public sandbox; production not yet available. |
Pink Agentic AI Payments | Pink sandbox API/MCP (by PinkWallet) | category_block | rule.payee = "cat:<category>" combined with action: "block" | not applicable | not applicable | API server-side (before a credential is issued) | https://pinkwallet.com/agentic/developers/policy-rules-reference/ | cat:blocked matches gift cards, crypto exchanges, cash-like and gambling by name. | 2026-10-02 | Publisher (PinkWallet), self-documented. Stage: early access / public sandbox; production not yet available. |
Pink Agentic AI Payments | Pink sandbox API/MCP (by PinkWallet) | single_use | issued credential (pink.get_credential): single-use virtual card or submitted bank transfer, locked to the payee and the amount | not applicable | not applicable (per-payment; valid 15 minutes) | API server-side (before a credential is issued) | https://pinkwallet.com/agentic/developers/security-model/ | a single-use virtual card locked to the payee and the amount, a bank transfer that is already submitted, or a platform refund reference. Each expires 15 minutes after issue. | 2026-10-02 | Publisher (PinkWallet), self-documented. Stage: early access / public sandbox; production not yet available. Sandbox card credentials use a 4111 1111 test-range BIN, never a real card. |
Pink Agentic AI Payments | Pink sandbox API/MCP (by PinkWallet) | human_approval | rule.action = "ask" with approvers ({people:[ids], n} or {group: id, n}) | not applicable | not applicable | API server-side (before a credential is issued) | https://pinkwallet.com/agentic/developers/policy-rules-reference/ | approvers {people:[ids], n} or {group: id, n} Named people, or a quorum of a group (for example 2 of 3 executives). | 2026-10-02 | Publisher (PinkWallet), self-documented. Stage: early access / public sandbox; production not yet available. |
Pink Agentic AI Payments | Pink sandbox API/MCP (by PinkWallet) | expiry | issued-credential expiry (15 minutes after issue); approval hold expiry on timeout, reported as "expired" | not applicable | 15 minutes (credential); configurable hold timeout (approval) | API server-side (before a credential is issued) | https://pinkwallet.com/agentic/developers/security-model/ | If nobody answers before the timeout, the hold expires and the agent is told expired . | 2026-10-02 | Publisher (PinkWallet), self-documented. Stage: early access / public sandbox; production not yet available. |
Pink Agentic AI Payments | Pink sandbox API/MCP (by PinkWallet) | revocation | not documented (pause stops the agent going forward; no separate per-credential revoke call described in the docs reviewed) | not applicable | not applicable | not stated on this page (see the agent-pause circuit breaker) | https://pinkwallet.com/agentic/developers/security-model/ | Paused agent: blocked. | 2026-10-02 | Publisher (PinkWallet), self-documented. Stage: early access / public sandbox; production not yet available. Pause is agent-level (blocks all future requests from that agent) with no approval path; a call to revoke one already-issued credential is not described in the docs reviewed for this check. |
Agentic AI Payments: Agent Spending Controls Crosswalk (2026) — by Pink Agentic AI Payments
Published by Pink Agentic AI Payments (by PinkWallet) — the approval layer between AI agents and company money: plain-language rules, per-agent budgets and human approvals decide each payment before it executes. Agents connect via MCP or REST. Try the free public sandbox: https://agentic-sandbox.pinkwallet.com (test credentials, no real money moves) · Product: https://pinkwallet.com/agentic/ · Examples: https://github.com/Pink-Agentic-Payments/sandbox-examples
As of v1.1.0, Pink is included as a row in
crosswalk.csvand in the summary table below, under the same evidence rules as every other row (quoted, sourced, mechanically checked — seequote-check.md). Pink's rows are self-documented by the publisher, labeled as such, and scoped to its early-access public sandbox (production not yet available). See "How Pink Agentic AI Payments compares" below.
Every payment provider and protocol that lets you cap what an AI agent can spend uses its own field names, units, and enforcement point — there is no shared standard. This crosswalk maps 14 providers/protocols (AP2, Stripe Issuing, Privacy.com, Lithic, AgentCard, Crossmint, Coinbase CDP, Circle, Tempo, Payman, Skyfire, x402, Visa Intelligent Commerce, Mastercard Agent Pay) + the publisher (Pink Agentic AI Payments) to the exact field or setting they document for amount caps, allowlists, category blocks, and approval requirements, each with a quoted source.
Also available on Hugging Face: https://huggingface.co/datasets/Agentic-Payment/agent-spending-controls-crosswalk (with the dataset viewer).
How Pink Agentic AI Payments compares
Counted directly from the ✓ marks in the summary table below: Pink documents 7 of the 8 control types in this crosswalk (per-tx cap, per-period cap, merchant/recipient allowlist, category block, single-use, human approval, expiry); it does not document a separate call to revoke one already-issued credential (an agent can be paused, which is a different, agent-level control — see the revocation row for Pink in crosswalk.csv). Among the other 14 providers/protocols, the most any single one documents is 5 (AgentCard: per-tx cap, per-period cap, allowlist, single-use, human approval).
That is a count of breadth across this crosswalk's 8 categories, not a quality ranking — see "Where Pink is behind" below, and judge every row, including Pink's, by its own quoted source in crosswalk.csv.
Depth the 8 columns don't capture. These are specific things Pink's own docs describe, cited so you can check them yourself — not claims about what other providers lack:
- Company-wide daily ceiling across all agents, checked as a circuit breaker before any rule runs: "Company daily ceiling. All agents together, per day." (policy-rules-reference)
- Ordered rules with a default-block fallback: breakers first, then rules top to bottom, first match wins, and anything no rule covers is blocked by default. (policy-rules-reference)
- n-of-m group approvers for a single rule, e.g. a documented example rule requiring 2 of 3 executives above $50,000:
"approvers": {"group": "g_exec", "n": 2}. (policy-rules-reference) - Payee-bank-change and duplicate-invoice fraud signals evaluated on every request regardless of amount, via
requires/absentevidence flagspayeeChangedanddupInvoice. (security-model, policy-rules-reference)
Where Pink is behind. Pink is early access: production is explicitly not available yet ("Sandbox live... Production is not yet available" appears across the developer docs), credentials are test values (a 4111 1111 test-range card BIN, sandbox bank-transfer references), and evidence flags like po/scan are self-asserted by the calling agent in the sandbox rather than verified against a connected ERP/warehouse system. Pink does not document a per-credential revocation call (see revocation row above) — only agent-level pause.
How to read the table
crosswalk.csv has one row per control (a provider may have several: a per-transaction cap, a merchant lock, an approval threshold, etc.). Columns:
- control_type — one of
amount_cap_per_tx,amount_cap_per_period,merchant_allowlist,category_block,single_use,human_approval,expiry,revocation,other - field_or_setting — the exact name as documented. Where a provider only describes a control in marketing language, with no API/schema field name published, this says
not documentedrather than guessing. - unit / period_options — minor units (cents), major units, USDC, currency-agnostic, etc., and any interval choices (daily/weekly/monthly/…), as stated by the source.
- enforcement_point — where the cap is actually checked: authorization-time at the card network, onchain, API server-side, or client-side SDK/CLI.
- evidence_url / verbatim_quote / accessed_date — the exact source and quote, so you can verify it yourself.
Summary: provider × control type
14 providers/protocols + the publisher (Pink Agentic AI Payments).
| Provider | Per-tx cap | Per-period cap | Merchant/recipient allowlist | Category block | Single-use | Human approval | Expiry | Revocation |
|---|---|---|---|---|---|---|---|---|
| Pink Agentic AI Payments (publisher; self-documented; sandbox stage) | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | — |
| AP2 | ✓ | ✓ | — | — | — | ✓ | — | — |
| Stripe Issuing | ✓ | ✓ | — | ✓ | — | — | — | — |
| Privacy.com | ✓ | ✓ | ✓ | — | ✓ | — | — | — |
| Lithic | — | ✓ | ✓ | ✓ | — | — | — | — |
| AgentCard | ✓ | ✓ | ✓ | — | ✓ | ✓ | — | — |
| Crossmint | — | — | — | — | — | — | — | ✓* |
| Coinbase CDP | ✓ | ✓ | — | — | — | — | — | — |
| Circle | ✓ | ✓ | ✓ | — | — | ✓ | — | — |
| Tempo | ✓ | ✓ | — | — | ✓ | — | ✓ | — |
| Payman | ✓ | ✓ | — | — | — | ✓ | — | — |
| Skyfire | ✓ | — | — | — | — | — | ✓ | — |
| x402 | ✓† | — | — | — | — | — | — | — |
| Visa Intelligent Commerce | — | — | — | — | — | — | — | — |
| Mastercard Agent Pay | — | — | — | — | — | — | — | — |
† x402: the upto scheme's authorized maximum is a per-request ceiling; maxAmountRequired (v1 exact) is a price set by the resource server, not a payer-side budget. Payer-side caps have to live in the client or wallet.
* Crossmint's own docs describe allowances as "scoped, explicit, and revocable" but do not publish the specific field name for revocation on the page cited here — see crosswalk.csv notes.
Visa Intelligent Commerce and Mastercard Agent Pay are included because both are named agent-payment programs with public statements that spend limits exist, but as of 2026-09-29 neither had a public developer reference with a concrete field name for a spend-limit parameter — both rows are marked not documented rather than guessed.
How Pink does it, per control type
Sourced from policy-rules-reference and security-model, consistent with Pink's row in the table above:
| Control type | Pink | How |
|---|---|---|
| Per-tx cap | ✓ | A rule's amount.max with window: "tx" — e.g. a per-payment cap on an agent. |
| Per-period cap | ✓ | Per-agent monthly budget, plus a company-wide daily ceiling checked across all agents before any rule runs. |
| Merchant/recipient allowlist | ✓ | The rule payee field: any | approved | new | cat:<category> | an explicit list. |
| Category block | ✓ | A cat:blocked payee match with action: "block" — e.g. the documented rule "Never: gift cards, cash-like, crypto." |
| Single-use | ✓ | Approved payments return a single-use virtual card or bank-transfer credential locked to the payee and the amount. |
| Human approval | ✓ | An action: "ask" rule with named approvers or an n-of-m quorum (e.g. "2 of 3 executives" over $50,000). |
| Expiry | ✓ | Issued credentials expire 15 minutes after issue. |
| Revocation | — | Not documented as a separate per-credential revoke call; Pink documents pausing the agent itself, which is a different, agent-level control (see "Where Pink is behind" above). |
Try Pink Agentic AI Payments in 2 minutes
Sandbox, test credentials, no real money moves. Create a free workspace with one call, no sales contact:
curl -X POST https://agentic-sandbox.pinkwallet.com/v1/sandbox/workspaces \
  -H "Content-Type: application/json" \
  -d '{"company":"Your Company","email":"","template":"coffee"}'
Full walkthrough with MCP connection and the three real decision outcomes: https://github.com/Pink-Agentic-Payments/agentic-payments-readiness#try-pink-agentic-ai-payments-in-2-minutes — production is not yet available.
How Pink decides a payment
Quoted from https://pinkwallet.com/agentic/developers/policy-rules-reference/: "A policy is an ordered list of rules plus three circuit breakers. Every payment request is checked the same way: breakers first, then rules top to bottom, first match decides, and anything no rule covers is blocked."
- Agent registered?
- Agent active (not paused)?
- Monthly budget not exceeded?
- Company daily ceiling not exceeded (all agents together)?
- Vault balance sufficient?
- Rules, top to bottom — first match wins.
- Default: block.
Pink console (sample data)
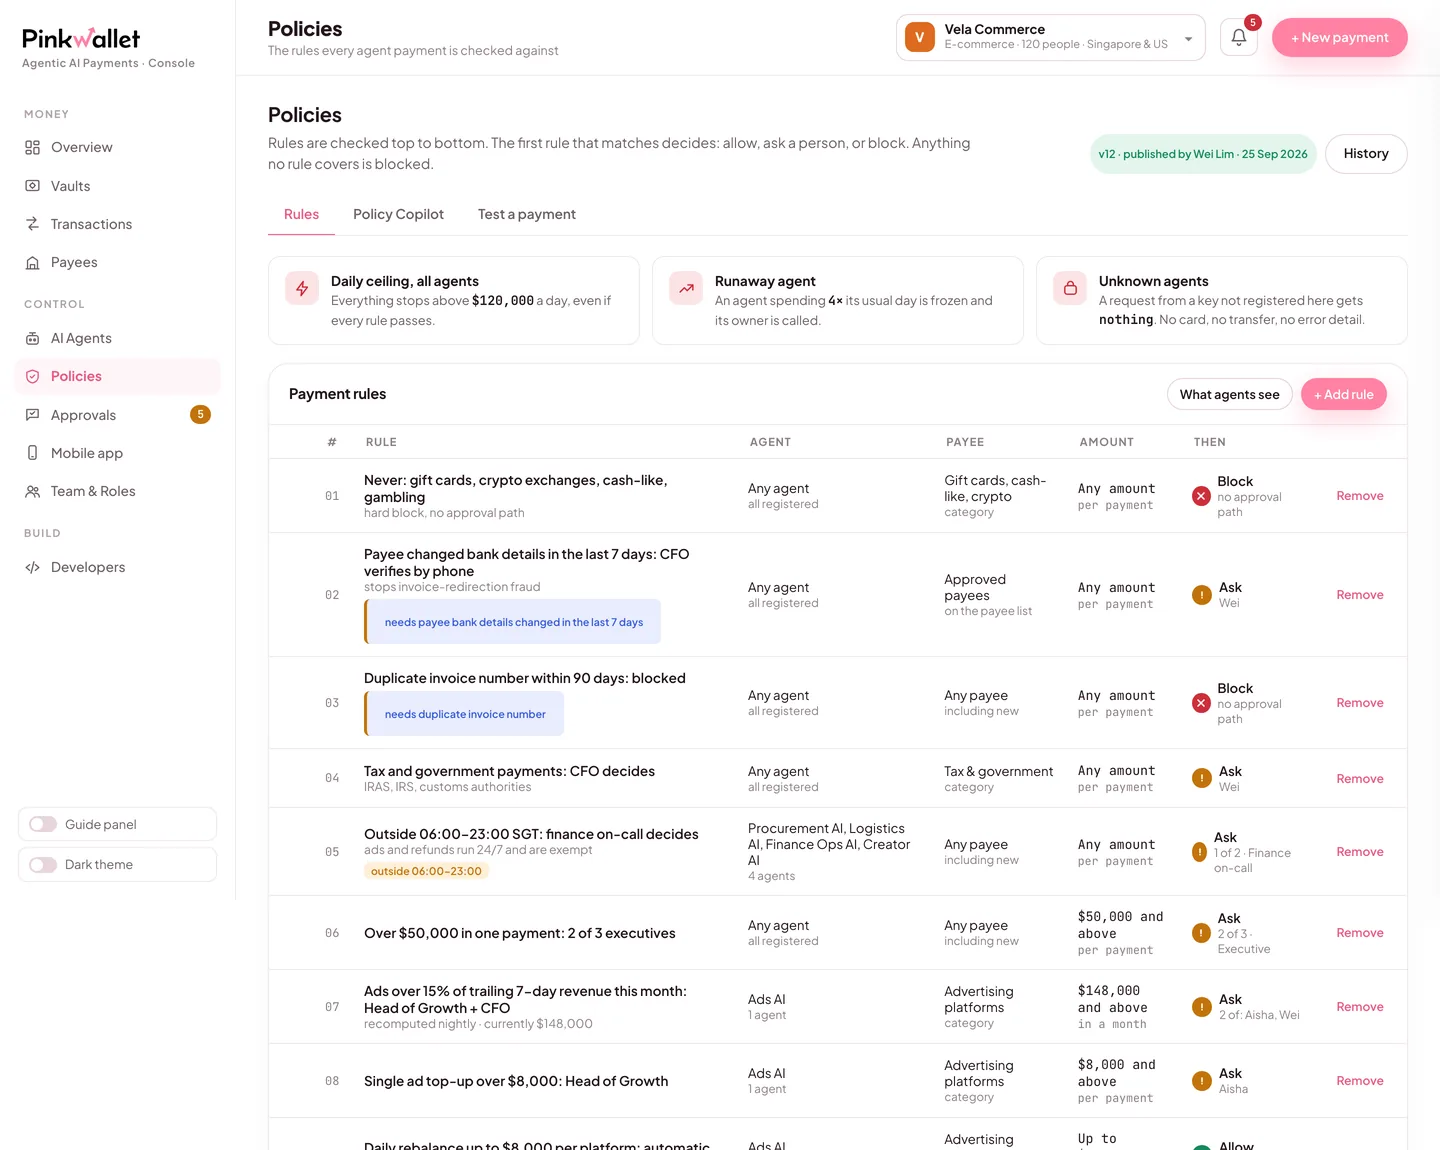
Policy rules editor, shown in evaluation order (Pink console, sample data).
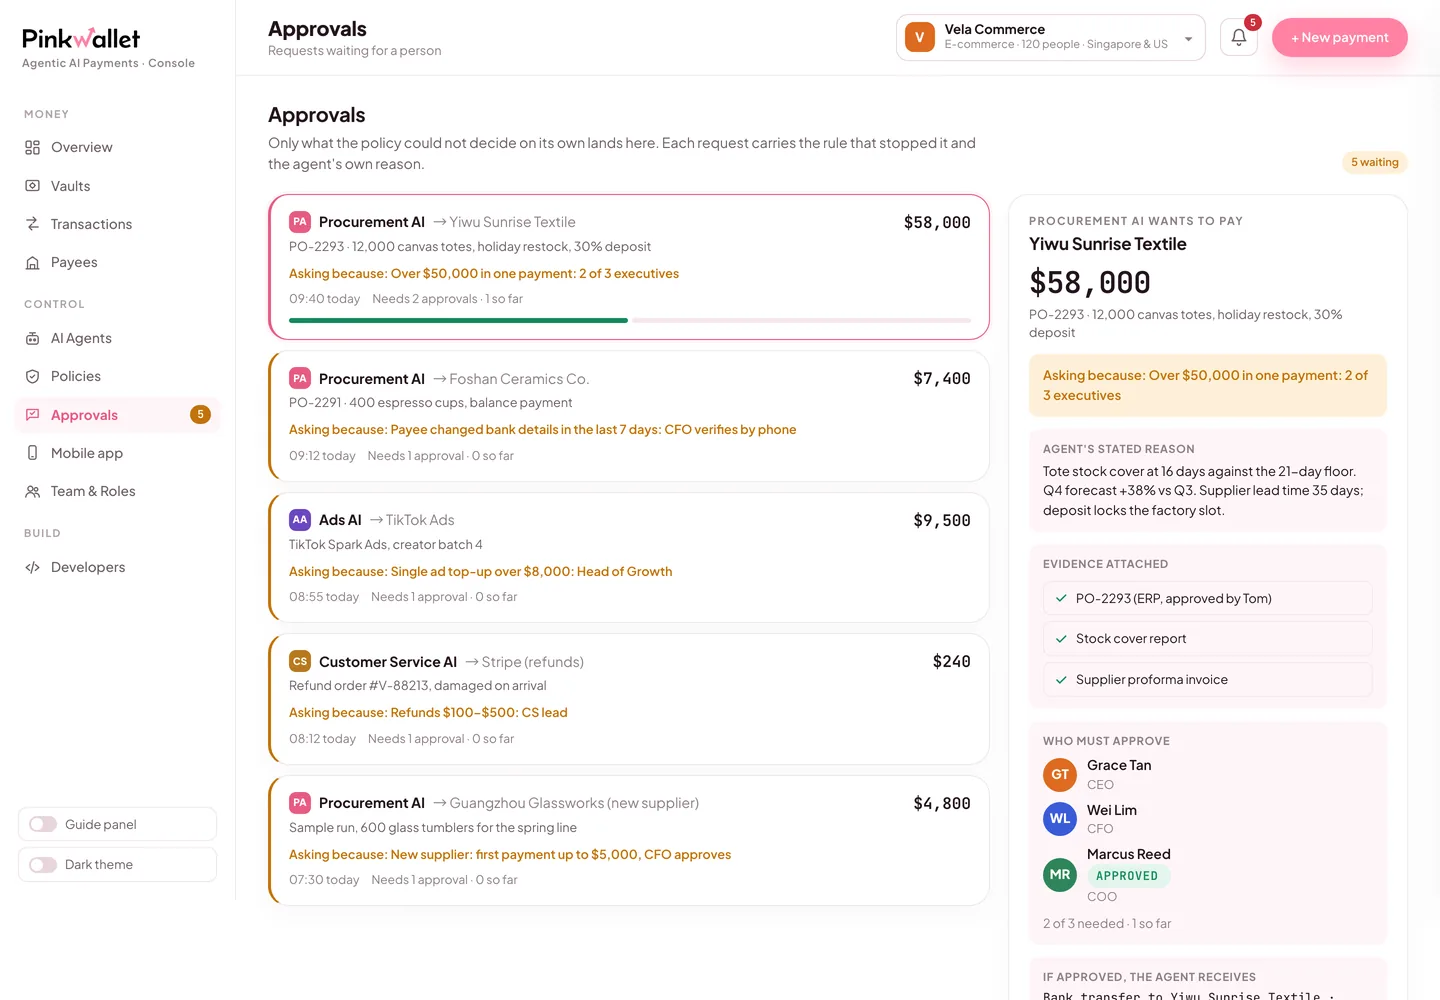
Pending "ask a person" approvals (Pink console, sample data).
Gotchas
- AP2's unit mismatch:
amount_range.maxis documented in the schema as minor units ("cents"), butbudget.maxhas no unit stated in its own schema text — the reference SDK'sBudgetEvaluatormultipliesbudget.maxby 100 to get minor units, implyingbudget.maxis actually in major units. This is a live discrepancy across AP2's own schema files, not a crosswalk error. Seecrosswalk.csvrows 2 and the source repo (pinned commite1ea56d). - Circle's monotonic rule: Circle's CLI enforces
per-tx ≤ daily ≤ weekly ≤ monthly— you cannot set a per-transaction cap higher than the daily cap, etc. - Circle's OTP handoff: raising or resetting a Circle agent-wallet limit requires a human-entered OTP in an interactive terminal; the agent is explicitly instructed not to see or relay it.
- x402's
amountis phase-dependent in theuptoscheme: the same JSON field means "authorized maximum" at verification time and "actual amount to charge" at settlement time — read the phase, not just the field name. - "Not documented" is common at the marketing layer: several programs (Coinbase CDP's TEE/enclave enforcement claims, Visa Intelligent Commerce, Mastercard Agent Pay) describe spend limits in prose without a public field-level schema. Don't assume a schema exists just because a blog post mentions "spending limits."
Methodology
Rows were kept only when a provider's own documentation, spec, or reference SDK/API stated the control — no third-party blog posts or unverified aggregator pages were used as primary evidence. Every verbatim_quote was mechanically substring-matched (whitespace-normalized) against the text of its evidence_url, fetched on 2026-09-29: GitHub-hosted specs (AP2, x402, Circle's circlefin/skills) were fetched via raw.githubusercontent.com at a pinned commit SHA so the quotes stay reproducible even if the repo changes; JS-rendered documentation sites (docs.lithic.com, docs.skyfire.xyz, developers.circle.com, tempo.xyz, docs.cdp.coinbase.com, docs.crossmint.com) were rendered with Playwright/Chromium before extraction. Two official pages (docs.paymanai.com, www.mastercard.com) were unreachable directly at check time (a Cloudflare origin SSL error and Akamai bot-blocking, respectively) — for those two rows only, a Wayback Machine snapshot of the same official page is cited instead, and the substitution is disclosed in the row's notes column. See quote-check.md for the full pass/fail table (42/42 kept rows passed; 6 rows that failed the mechanical check were dropped rather than fixed by hand). A review pass on 2026-09-29 replaced the Stripe Issuing evidence with the spending-controls guide (https://docs.stripe.com/issuing/controls/spending-controls) and added a per_authorization row: 43 rows in total. In v1.1.0 (2026-10-02), 8 rows for the publisher, Pink Agentic AI Payments, were added under the same rules — fetched live, mechanically quote-checked (8/8 passed, see quote-check.md), and labeled self-documented in notes: 51 rows in total.
Conflict of interest
Published by Pink Agentic AI Payments (by PinkWallet, early access) — see the note at the top of this README. Pink is included in crosswalk.csv as of v1.1.0, under the same evidence rules as every other row: self-documented by the publisher, quoted, sourced, and mechanically quote-checked (see quote-check.md), with notes on every Pink row stating "Publisher (PinkWallet), self-documented."
Try the free public sandbox (test credentials, no real money moves): https://agentic-sandbox.pinkwallet.com
Related PinkWallet datasets
License
CC BY 4.0 — reuse with attribution.
Corrections
Found a stale field name, a wrong unit, or a provider that's changed its docs? Open an issue with the URL and the exact quote you're disputing.
Changelog
- v1.2.0 (2026-10-02): expanded publisher (Pink) sections — a "How Pink does it" note per control type under the summary table, a 2-minute trial block, the decision order, and 2 console screenshots. No data changes for other providers.
- v1.1.0 (2026-10-02): added the publisher (Pink Agentic AI Payments) under the same evidence rules; title updated; no other rows changed.
- v1.0.0 (2026-09-29): initial release, 43 rows across 14 providers/protocols.
- Downloads last month
- 71